
Certification
SIAS badge rules
A SIAS badge is valid only when it links to an Active verification record. These rules keep badges honest. The full policy is part of every holder’s badge license.
Every badge links to its record
Holders display the badge as a link to its own verification page, using the image hosted by SecurityInspect, which changes automatically if the certificate’s status changes. In documents and print, the verification address is printed next to the badge.
Each certificate has one record at securityinspect.com/verify/ followed by its certificate ID, and the badge links straight to it: no redirects, link shorteners or tracking wrappers. Certification is valid only when the linked verification record confirms an Active status.
The embed code for a horizontal badge looks like this, shown with the reserved specimen ID:
<a href="https://securityinspect.com/verify/SIAS-0000-0000-0000-0000">
  <img src="https://securityinspect.com/badge/SIAS-0000-0000-0000-0000.svg"
       alt="SecurityInspect Certified — independently assessed against SIAS v1.0. Select to verify current status."
       width="352" height="100">
</a>Who can display a badge
- Only SecurityInspect Certified and SecurityInspect Verified lead to a certificate and a badge.
- A SecurityInspect Verified badge, and any statement about it, always says “limited technical scope”. SecurityInspect Reviewed has no badge.
- No one may display a badge before a certification decision, or after a certificate stops being Active.
How a badge must look
Only the supplied light and dark versions of the horizontal, seal and compact layouts, at or above the minimum size, with clear space around them. No recoloring, cropping, stretching, animation, added words or effects.
| Layout | Native size (CSS px) | Minimum on screen | Intended use |
|---|---|---|---|
| Horizontal | 352 × 100 | 288 px wide | Trust, security and product pages |
| Seal | 176 × 176 | 160 px wide | Where a round mark fits; documents |
| Compact | 140 × 50 (SecurityInspect Verified: 140 × 62) | 120 px wide | Website footers |
The alternative text for the SecurityInspect Certified badge is fixed:
SecurityInspect Certified — independently assessed against SIAS v1.0. Select to verify current status.
Specimen badges
These specimens show every supplied layout. Each carries the reserved ID SIAS-0000-0000-0000-0000, which is never issued, and a band that reads “Specimen — not a real certificate”. A real badge carries its own certificate ID and links to its own record.
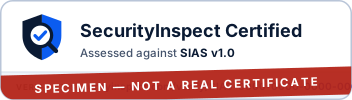 Horizontal
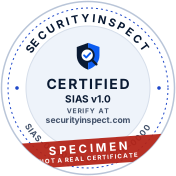 Seal
 Compact
 Horizontal
 Seal
 Compact
 Horizontal
 Seal
 Compact
 Horizontal
 Seal
 Compact
Where a badge may appear
Where it clearly refers to the certified scope, and on websites only on the domains listed on the verification record. When a page covers more than the scope, the badge carries a line saying what is covered. Badges are never shown in a row of HIPAA, PCI, SOC or ISO logos, and are never combined with any other framework’s name or mark.
What framework mappings mean
SecurityInspect certification is a proprietary, scope-limited assessment against the SecurityInspect Assurance Standard. Framework mappings indicate thematic alignment only. Certification does not constitute an HHS-recognized HIPAA certification, PCI DSS validation, a SOC 2 examination or report, or accredited ISO/IEC 27001 certification.
What holders may say
Holders may say that they hold SecurityInspect Certified (or SecurityInspect Verified, with its limited technical scope) for the stated scope, with a link to the record. They may not describe themselves as secure, compliant or guaranteed on the strength of a certificate, or suggest that SIAS is a HIPAA, PCI DSS, SOC 2 or ISO/IEC 27001 outcome.
When a certificate stops being Active
The hosted badge changes to “Not currently active” straight away, but the text that describes the badge in the holder’s own page code does not, so holders remove the embed code as well.
- Expiry: every badge, embed and certification claim comes down by the end of the expiry date (23:59:59 UTC). Suspension, revocation or an unplanned withdrawal: web and digital uses come down as soon as the holder receives our notice, and printed materials stop being handed out. The certificate is not valid from the moment its status changes.
- Badge images aren’t used in email signatures, because a sent email can’t be updated. Holders may add a plain text line with the verification link instead.
Misuse
Misuse can lead to suspension or revocation. To report a badge that looks wrong, use the contact form and choose the topic “SIAS certification”. Report a badge that looks wrong
| What was done | Why it is misuse |
|---|---|
| Badge image with no link | A visitor can’t check the status; the badge becomes an unverifiable claim |
| Badge linked to the SecurityInspect home page | It doesn’t lead to the certificate |
| A downloaded image on a website instead of the hosted image | It won’t change when the status changes |
| Badge recolored to the holder’s brand color | Recoloring is prohibited |
| Badge in a row with HIPAA, SOC 2 and ISO logos under “Our certifications” | It suggests SIAS is part of, or equal to, those programs |
| “HIPAA compliant” added under the badge | It adds wording and implies a framework claim |
| Alternative text changed to “Certified secure” | It changes fixed text and makes a prohibited claim |
| SecurityInspect Verified badge in a site-wide header, with no scope line | It presents a limited technical scope as organizational certification |
| Badge still on the website the day after the certificate expired | Use after expiry: the expiry date was known a year ahead |
| Staff profile headline “SecurityInspect Certified professional” | SIAS never certifies a person |
| Badge on a subsidiary’s website that isn’t listed on the record | It is outside the certified scope and not a bound domain |
| Screenshot of the verification page used as proof months later | The status may have changed; screenshots are not records |
| A “SIAS in progress” seal during an assessment | No badge exists before a decision |
| Link to the verification page through a URL shortener | It hides the destination |
| Badge shown for a SecurityInspect Reviewed outcome | Reviewed never gets a badge and doesn’t indicate a pass |
| Hosted badge image in an email signature | Sent emails can’t be updated, and blocked images keep showing the alternative text |
Where our work stops
Security Inspect is not a law firm or a CPA firm and does not provide legal opinions or issue SOC 2 reports. ISO/IEC 27001 certification is performed independently by an accredited certification body. CMMC organization-level assessment authority depends on an active C3PAO listing. Specific PCI services depend on the company’s active PCI SSC program listing and scope.
Talk to us about a SIAS assessment
Tell us what you want assessed, and we’ll start with the scope.